You should have already created an account for the Blocklists via DNS Query as described here in the RBL page.
Installing the plugin for SpamaAssassin
First of all let's disable the ordinary queries by adding the following to /etc/mail/spamassassin/local.cf:
# disable Spamhaus
score URIBL_DBL_SPAM 0
score URIBL_DBL_PHISH 0
score URIBL_DBL_MALWARE 0
score URIBL_DBL_ABUSE 0
score URIBL_DBL_ABUSE_REDIR 0
score URIBL_DBL_ABUSE_PHISH 0
score URIBL_DBL_ABUSE_MALWARE 0
score URIBL_DBL_BLOCKED 0
score URIBL_DBL_BLOCKED_OPENDNS 0
# disable DNSWL
score RCVD_IN_DNSWL_BLOCKED 0
score RCVD_IN_DNSWL_MED 0
score RCVD_IN_DNSWL_HI 0
score RCVD_IN_DNSWL_LOW 0
Download the latest package:
git clone https://github.com/spamhaus/spamassassin-dqs
Things go in a slightly different way when the HBL dataset is enabled (it's not enabled for free accounts).
Enter the 4.0.0+ folder and run the test to confirm that our key is valid also for HBL (this doesn't mean that it's enabled as well):
sh hbltest.sh
	Please input your DQS key: xxxxxxxxxxxxxxxxxxxxxxxxxxxx
	Looking up test record for HBL... done
	Your DQS key xxxxxxxxxxxxxxxxxxxxxxxxxxxx is enabled for HBL
	You can copy sh_hbl.cf and sh_hbl_scores.cf if you want HBL enabled
Now you have to insert the content of the key in a couple of config files (replace xxxxxxxxxxxxxxxxxxxxxxxxx with the content of the key):
sed -i -e 's/your_DQS_key/xxxxxxxxxxxxxxxxxxxxxxxxxxx/g' sh.cf
sed -i -e 's/your_DQS_key/xxxxxxxxxxxxxxxxxxxxxxxxxxx/g' sh_hbl.cf
For FreeBSD users the commands are the following:
sed -i "" -e 's/your_DQS_key/xxxxxxxxxxxxxxxxxxxxxxxx/g' sh.cf
sed -i "" -e 's/your_DQS_key/xxxxxxxxxxxxxxxxxxxxxxxx/g' sh_hbl.cf
If HBL is not enabled, you can just copy the two following files in the SpamAssassin's configuration directory:
cp sh.cf sh_scores.cf /etc/mail/spamassassin
Now proceed below in the test section.
If HBL is enabled, edit the file sh.pre in the first line:
loadplugin Mail::SpamAssassin::Plugin::SH <config_directory>/SH.pm
Now replace <config_directory> with the config dir, which is /etc/mail/spamassassin. Therefore the line becomes:
loadplugin Mail::SpamAssassin::Plugin::SH /etc/mail/spamassassin/SH.pm
If HBL is enabled, assuming that the config dir is sia /etc/mail/spamassassin, copy there the config files:
cp SH.pm sh.cf sh_scores.cf sh_hbl.cf sh_hbl_scores.cf sh.pre /etc/mail/spamassassin
Now enable HBL by editing the file /etc/mail/spamassassin/v342.pre. You have to find the line:
loadplugin Mail::SpamAssassin::Plugin::HashBL
and eventually remove the initial #.
Restart SpamAssassin:
spamdctl restart
Test the setup in this way:
spamassassin --lint
if you don't get any output then the test went well.
Testing the filter
Navigate to https://blt.spamhaus.com/ and insert a valid email address. Then add the DQS key and run the tests:
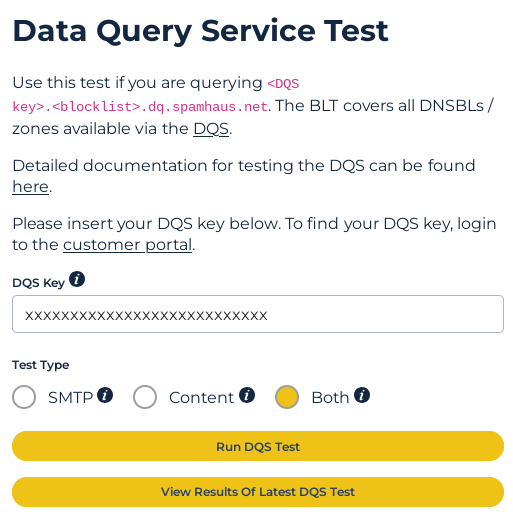
You'll get something like this:
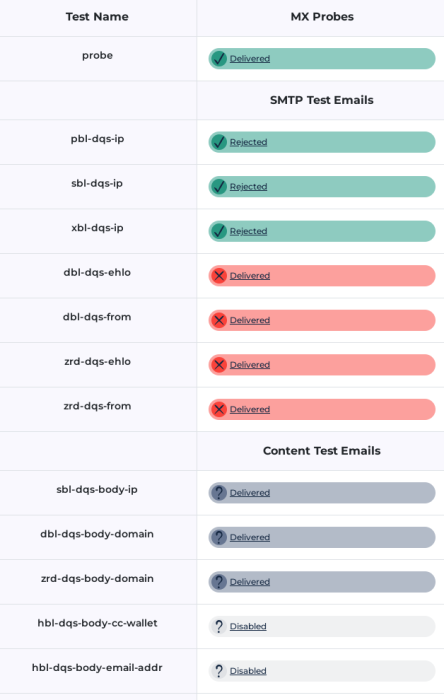
In the above example HBL is disabled, while messages with DBL ande ZRD tests apparently failed. Be sure that DBL and ZRD tests have been rejected by SpamAssassin, by checking the junk folder:
Content analysis details:   (19.5 points, 5.0 required)

 pts rule name              description
---- ---------------------- --------------------------------------------------
 0.7 SPF_HELO_SOFTFAIL      SPF: HELO does not match SPF record (softfail)
-0.0 BAYES_20               BODY: Bayes spam probability is 5 to 20%
                            [score: 0.0573]
 0.0 DMARC_MISSING          Missing DMARC policy
 2.8 TXREP                  TXREP: Score normalizing based on sender's reputation
 8.0 SH_DBL_HEADERS         A domain found in headers (mail from, reply-to etc..)
                            is listed in DBL
                            [dbl-dqs.blt.spamhaus.net]
 8.0 SH_DBL_BODY            The domain of an email address found in body is listed in
                             DBL
                            [dbl-dqs.blt.spamhaus.net]
Content analysis details:   (12.1 points, 5.0 required)

 pts rule name              description
---- ---------------------- --------------------------------------------------
-0.0 SPF_HELO_PASS          SPF: HELO matches SPF record
 8.0 SH_HELO_ZRD_VERY_FRESH The domain used in the HELO string is listed
                            in ZRD and the domain age is between 0 and 4
                            hours
                            [zrd-dqs.blt.spamhaus.net]
-0.0 BAYES_20               BODY: Bayes spam probability is 5 to 20%
                            [score: 0.1579]
 1.0 FORGED_SPF_HELO        No description available.
 0.4 KHOP_HELO_FCRDNS       Relay HELO differs from its IP's reverse DNS
 0.0 DMARC_MISSING          Missing DMARC policy
 2.7 TXREP                  TXREP: Score normalizing based on sender's reputation